We build the compliance layer that makes regulated AI deployment possible.
ZeroDrift was founded in 2023 after the team spent years watching enterprise AI projects stall or get cancelled due to a single, unresolved problem: there was no reliable way to enforce policy on AI output at scale.
Why we built ZeroDrift.
Before starting ZeroDrift, I spent years building model deployment infrastructure for a regulated customer base. The pattern I kept running into was the same: an AI assistant would pass every internal safety review, pass QA, pass staged rollout, and then six months into production, surface a response that triggered a compliance escalation. Not because the review was careless, but because the review process is static and AI outputs are not.
Prompt constraints hold in controlled conditions. Under real user inputs, edge cases accumulate. A user in a regulated context gets a response that would be fine on a consumer product but is a problem for their account type. A slightly different phrasing of a standard question produces an output that sits in a gray area no one thought to test. These are not model failures. They are enforcement failures, and they happen because there is no persistent inspection layer between the model output and the user.
We started building ZeroDrift in San Francisco in 2023 with one thesis: the right place to enforce policy is not in the model and not in the prompt, but in a proxy layer that sits between the model and every response. The enforcement logic has to be inspectable, versionable, testable, and fast enough to be invisible to users. We built for that constraint before anything else.
The teams that work with us are not looking for AI content moderation. They need a compliance layer they can explain to a regulator. That distinction shapes every product decision we make.
The people building ZeroDrift.
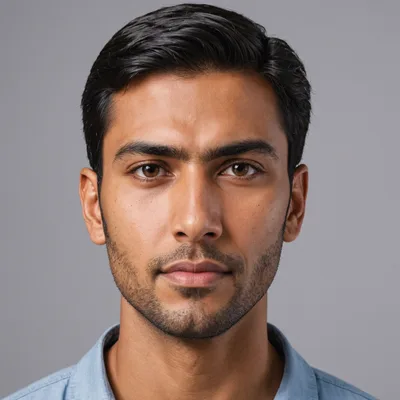
Kumesh Aroomoogan
CEO, Co-Founder
Built API gateway and access control systems for regulated industries, spending years managing model deployment pipelines for regulated customers. Founded ZeroDrift after repeatedly watching enterprise AI projects stall at compliance review, a problem he decided needed a dedicated enforcement layer rather than better prompting.
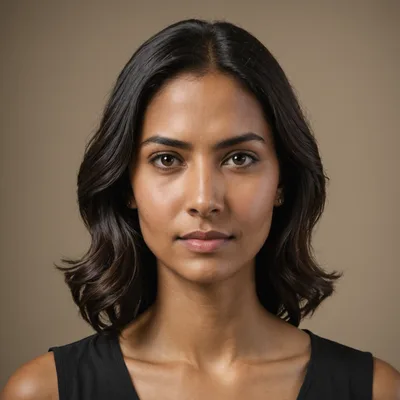
Priya Nambiar
Co-Founder, CTO
Career focused on high-throughput inference infrastructure: request routing, latency optimization, and the operational complexity of running model serving at production load. Designed the ZeroDrift proxy architecture with a hard constraint of sub-30ms policy evaluation, treating latency as a first-class requirement rather than a tuning parameter.
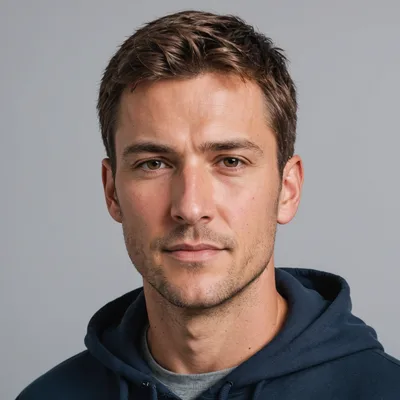
Marcus Delacroix
Head of Policy Engineering
Comes from a background in enterprise risk and model governance at two financial technology companies. Built internal policy review tooling before joining ZeroDrift to lead product design for the policy engine and audit trail. His background shapes how ZeroDrift thinks about compliance workflows, not just technical enforcement.
The principles that guide our decisions.
Enforcement over aspiration
Policies only matter when they are enforced on every request, not audited after the fact. We build tools that make enforcement the default state, not an option you have to configure.
Transparency in the audit trail
When a compliance team needs to explain what happened with a specific AI response, they should be able to. The audit trail is not a log for engineers. It is a document your legal team can use.
Latency is not a tradeoff
We built ZeroDrift on the assumption that teams will not accept a compliance layer that slows their product. Sub-30ms intercept was a design constraint from the first prototype, not a later optimization.